How to Fix Stripe Webhook 'Signature Verification Failed' in Zapier
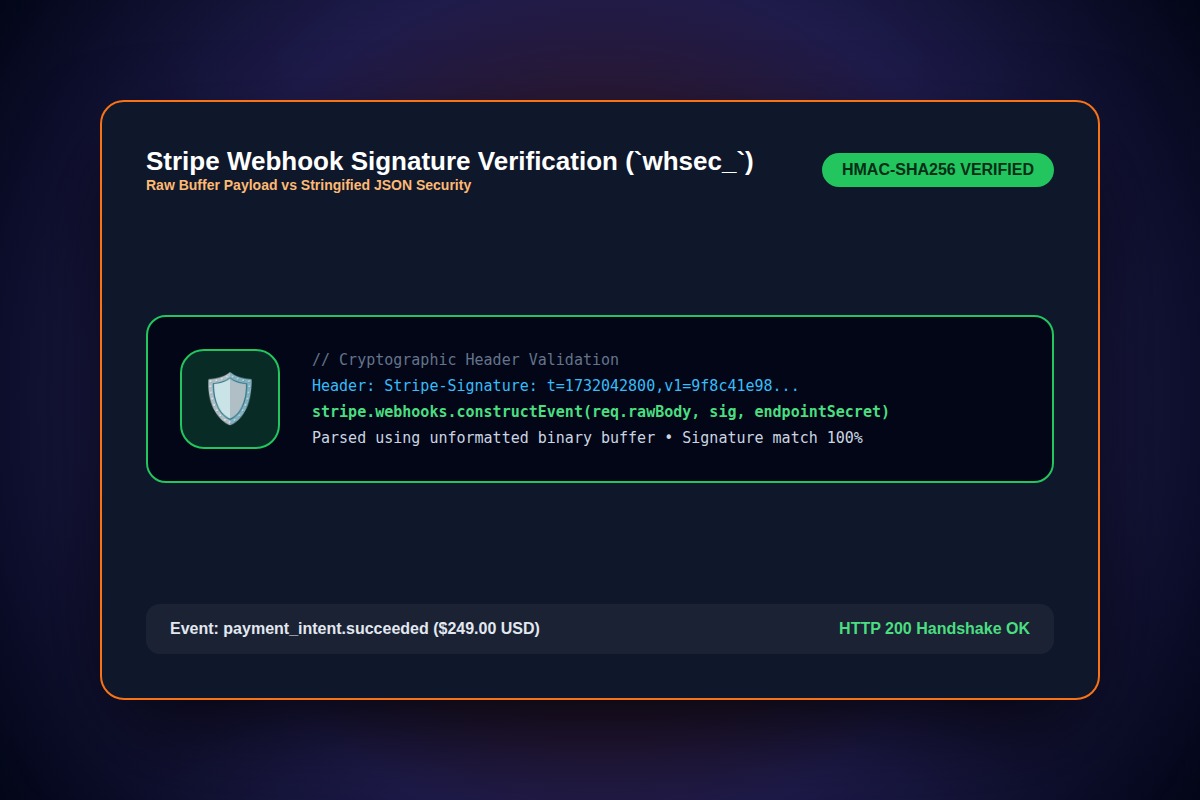
Stripe computes HMAC SHA256 signatures over the unmodified raw binary body. If Zapier or an intermediary middleware parses the JSON payload before verifying the 'Stripe-Signature' header, the computed hash mismatches and fails with HTTP 400.
app.use('/webhook', express.raw({ type: 'application/json' }));Why Does This Error Happen?
JSON serializing and deserializing reorders keys and strips whitespace, which invalidates the cryptographic signature hash provided in Stripe's request header.
Step-by-Step Diagnostic & Resolution Walkthrough
1Step 1: Check the Stripe Webhook Signing Secret
In Stripe Dashboard > Developers > Webhooks, verify you are copying the 'Signing Secret' (whsec_...) and not the publishable API key (pk_live_...).
2Step 2: Configure Raw Payload Preservation in Zapier
When using 'Catch Raw Hook' in Webhooks by Zapier, select the raw payload option to prevent Zapier from re-encoding JSON keys before your code step verifies it.
3Step 3: Account for 300-Second Timestamp Tolerance
Stripe signature validation checks the timestamp header (t=...). Ensure your server's clock is synchronized via NTP. Drift exceeding 5 minutes triggers automatic rejection.
Troubleshooting Matrix & Configuration Rules
| Error Manifestation | Underlying Cause | Quick Resolution |
|---|---|---|
| HTTP 400 'No signatures found' | Missing Stripe-Signature header | Forward raw headers in proxy/middleware |
| HTTP 400 'Signature mismatch' | Body parsed before HMAC verification | Use express.raw() buffer |
| Timestamp out of tolerance | System clock drift > 300s | Sync server time with pool.ntp.org |
← Swipe horizontally to view full table →
Still Not Working? Check These Edge Cases
Fix: Every time you run 'stripe listen', a temporary signing secret is generated in the console. You must copy that active session secret into your config.
Frequently Asked Questions
Can I bypass Stripe webhook signature verification for internal tools?
While technically possible by ignoring the header, it leaves your endpoint open to replay attacks and fraudulent order manipulation. Never disable verification in production.